Blog information security

Interview with ISO 27001 audit expert Philip Ku
Philip Ku is an international information security and audit expert. He is a certified lead auditor for ISO 27001 information security and also for related standards and trains auditors worldwide, including in The Netherlands. We interviewed Philip to understand how he became an expert and what he sees as new trends in information security.
Sieuwert van Otterloo
A summary of ISO 27001 requirements for information security
ISO / IEC 27001 is an official standard for the information security of organisations. Regrettably the standard is not freely available, making it harder than necessary to look up what is actually required by ISO 27001. This has led to some misconceptions. While we still recommend you to read the full standard, we decided to create a good summary to…
Sieuwert van Otterloo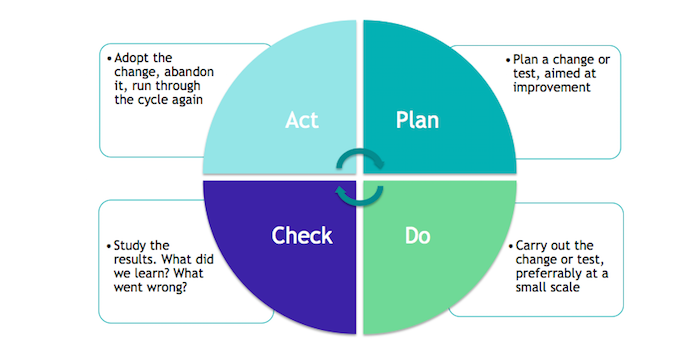
Information security and PDCA (Plan-Do-Check-Act)
Standards such as ISO 27001 require you to use a method for continuous improvement in your information security policy. PDCA or Plan-Do-Check-Act is the preferred method for most information security teams and we recommend you to use this method, described in this article.
Sieuwert van Otterloo