Blog Security

Access Management: an introduction
You can have the best XDR solutions out there, but if your data bucket is openly reachable online or a guest account is still active after years, these technological controls are not really protecting you. For instance, the top risks for web apps are broken access control and security misconfiguration. This is where IAM comes…
Pavlo Burda
A basic risk management method for information security
One of the requirements for good information security is to have a method for risk identification and assessment. This article describes one simple and practical method that can be used by any organisation. This page is part of a series on ISO 27001 controls and our free ISO27001 and GDPR templates.
Sieuwert van Otterloo
ICT Institute is now a Vanta partner: what users told us
At ICT Institute, we support customers with all kind of tooling: classic self-contained templates, Google Workspace, Notion and now Vanta. For our clients that work towards ISO 27001, we can now combine our hands-on ISMS advice (scoping, risk workshops, internal audits) with a compliance platform that takes a lot of the manual effort of collecting…
Pavlo Burda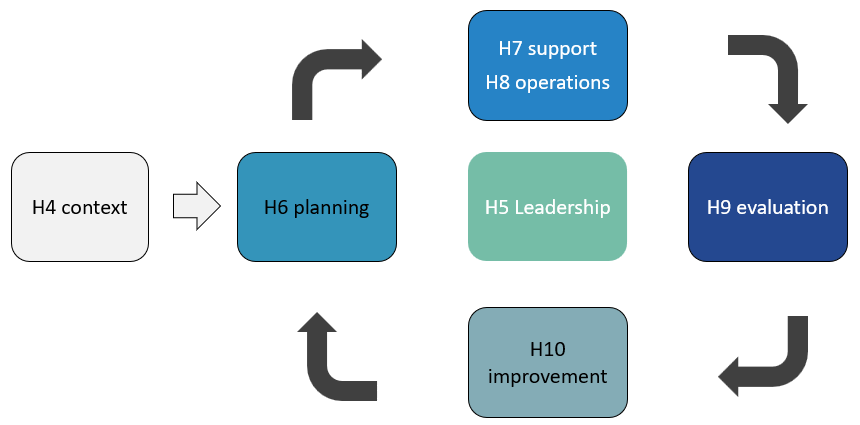
The ISO 27001 Harmonized Structure
In this article, we walk through the Harmonized Structure of the ISO 27001 (Chapters 4-10) and explain how to implement it using the Plan-Do-Check-Act (PDCA) cycle. This will be the basis for your Information Security Management System (ISMS) according to the standard. The “engine” of the ISMS: Chapters 4 to 10 ISO 27001 is structured…
Pavlo Burda
What documentation do you need for ISO 27001?
If you want an external auditor to certify your information security management system, you need to store documentation of for all elements in your policy. To make audits to go swiftly and smoothly, you should store all documented information in one easy-to-access place. In this post we provide an overview of what information needs to be stored and…
Sieuwert van Otterloo