Free online expert session: AI policy – Dec 17
| Sieuwert van Otterloo |
Artificial Intelligence
Many companies have decided they need to instruct their staff on how AI can and cannot be used in their organisation in the form of an AI policy. In this free online webinar people from ICT Institute and participants can share their questions and suggestions on suitable AI rules. The session is online, free of charge and open to any professional with either information security, privacy or AI experience.
Why this expert session
AI models and AI agent have become so good at many tasks that many people can outsource part of their work to AI. AI can be used to draft memos, summarize meetings, generate illustrations but also for summarizing confidential data, make business decision making of develop software.
On the one hand this is great news, since it should lead a boost in productivity. Some companies therefore encourage their staff to experiment with AI. On the other hand it leads to problems, such as mistakes and hallucinations, AI-slop, intransparency on what people did or did not read and potentially also bias and discrimination. Most companies therefore also want to introduce rules to limit the use of AI and to enforce transparency.
The goal of this session is to exchange ideas from all sources: from ICT Institute, publicly available guidelines but also from each participant. Each participant can share their questions and concerns and hear from other people which rules their organisation adopts.
How to participate
The event will take place online via google meet, on Dec 17, 15.00 – 16.30. To participate you must send an email to sieuwert at ictinstitute.nl and if you are indeed have a relevant security or privacy role we will add you to the session invite. There is a limit of max 12 participants.
Session format
Agenda:
- Sieuwert will give a brief introduction of recent AI incidents and examples rules adopted by ICT Institute.
- Next we will ask participants to share questions and suggestions and structure the rest of the sessions to discuss the questions and suggestions from participants.
- The session will end with a brief conclusion at 16.20 and close at 16.30
In the session we encourage people to share examples from their organisation so that other people can learn from them. Other people should treat the examples as somewhat confidential: they can tell people about the examples shared, but without disclosing company or personal names. This is often called Chatham house rule.
Suggested / expected topics
Based on our experience, many organisations have adopted AI policies to address the following issues
- Shadow AI: How do you prevent users from using unauthorised AI tools such as chatGPT, thus bypassing the company selection process.
- AI related data breaches: How can you prevent confidential data being shared with AI, and what process is needed to handle incidents
- AI literacy training: This is required under the AI Act and can be organised in different ways. We have a standard AI literacy training but would like to hear from other organisations.
- AI transparency: When should people disclose when a document was created with AI assistance? How does this differ between fully AI generated documents and human-written, AI-enhanced documents?
- AI supply chain: How do you select what AI suppliers to choose? Do you use self-hosted open weights models? This topic is very much linked to ISO 27001 supplier management but additional rules might be needed.
- AI in software development: How many manual review do you do on AI generated code? What guardrails or harness do you put in place to avoid AI coding mistakes?
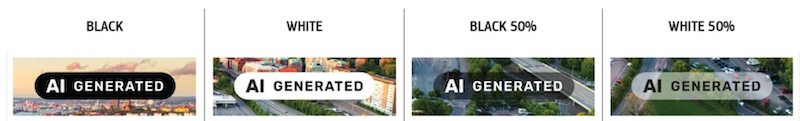
- The EU has developed a Code of Practice on transparency for AI generated content. It contains example logos as shown below.
Examples and further reading
Many public organisations have already published AI guidelines that can be used as a source of inspiration. If you are interested in AI policies we recommend the following resources:
- ICT Institute Responsible AI Use Policy 2026: This is a somewhat restrictive policy designed for consulting services and audits. For these services the use of AI is restricted to make sure clients get the service they expect.
- The emergence of generative artificial intelligence (GAI) has prompted the Dutch Organisation for Scientific Research NWO to develop a policy framework for the use of GAI: NWO Generative AI policy.
- AI Coding Rules (https://aicodingrules.org/) is a new initiative to explore the fragmented landscape of AI coding agent rules and proposes a unified standard to enable interoperability, quality, and security in AI-assisted software engineering.
- Google’s rules for AI during their Summer of Code Program: https://developers.google.com/open-source/gsoc/resources/ai_guidance
For high risk AI systems it is often required to do Fundamental Rights Risk Assessment as we explain using an example Fundamental Rights Risk Assessment (FRIA)AI Act: Fundamental Rights Impact Assessment (FRIA).
image source: Zach M via Unsplash

Dr. Sieuwert van Otterloo is a court-certified IT expert with interests in agile, security, software research and IT-contracts. He is a also an ISO 27001 and NEN 7510 auditor and AI researcher.