Author Pavlo Burda

Dr. Pavlo Burda is an IT consultant and researcher specializing in emerging cybersecurity threats and people analytics for security.

VU Computer Science Business Track results 2026
Students of the Vrije Universiteit Amsterdam, bachelor Computer Science, have the option to graduate via the ‘Business Track’. A special graduation program with more team work, more support and real topics from real companies. In 2026 more than 20 students were selected for the business track and completed their this project. Once again we are…
Pavlo Burda
Access Management: an introduction
You can have the best XDR solutions out there, but if your data bucket is openly reachable online or a guest account is still active after years, these technological controls are not really protecting you. For instance, the top risks for web apps are broken access control and security misconfiguration. This is where IAM comes…
Pavlo Burda
ICT Institute is now a Vanta partner: what users told us
At ICT Institute, we support customers with all kind of tooling: classic self-contained templates, Google Workspace, Notion and now Vanta. For our clients that work towards ISO 27001, we can now combine our hands-on ISMS advice (scoping, risk workshops, internal audits) with a compliance platform that takes a lot of the manual effort of collecting…
Pavlo Burda
Implementing ISO 42001: example audit report
In our previous article on the AI Risk Management System, we explained how an AIMS can help organizations structure AI governance and support compliance efforts with the AI Act. Here we introduce our new template for auditing and structuring your AIMS and prepare for ISO 42001 certification. What is the AIMS? ISO 42001 requires organizations…
Pavlo Burda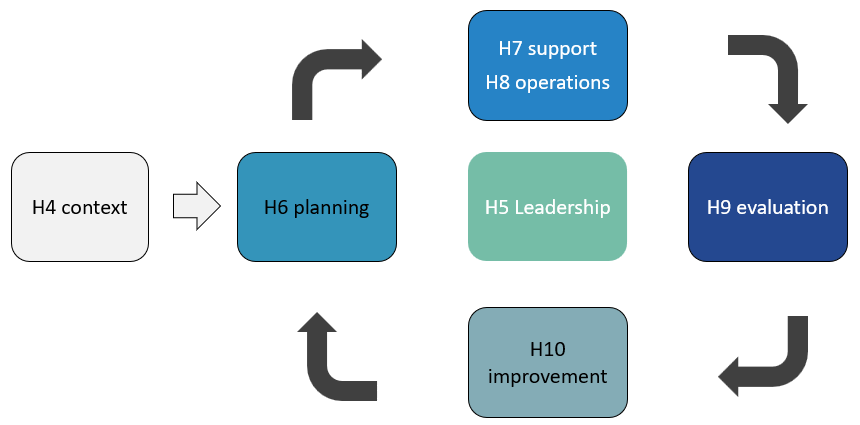
The ISO 27001 Harmonized Structure
In this article, we walk through the Harmonized Structure of the ISO 27001 (Chapters 4-10) and explain how to implement it using the Plan-Do-Check-Act (PDCA) cycle. This will be the basis for your Information Security Management System (ISMS) according to the standard. The “engine” of the ISMS: Chapters 4 to 10 ISO 27001 is structured…
Pavlo Burda