Blog Security
Code analysis prevents hidden security risks
Ensuring security in software means starting at the source code: Developers must build security in from the start. Organisations too often focus on repairing damage post-breach and fixing bugs after launch. Greater attention to security in the earlier stages of software development is needed. It would greatly reduce the percentage of successful attacks, and minimize damage when malicious hackers do…
Stephen Morrow
Interview with ISO 27001 audit expert Philip Ku
Philip Ku is an international information security and audit expert. He is a certified lead auditor for ISO 27001 information security and also for related standards and trains auditors worldwide, including in The Netherlands. We interviewed Philip to understand how he became an expert and what he sees as new trends in information security.
Sieuwert van Otterloo
No More Ransom: the best anti-ransomware available
No More Ransom is both the name and the endgoal for a cooperation between the Dutch police and several security companies like McAfee and Kaspersky. The project has been running for more than a year now, and is becoming quite successful in fighting ransomware – but is it enough to fight the currently so devastating flood of…
Tijs Hofmans
ISO 27001 Lead Auditor training November 20-23
It is important and often mandatory for organisation with a security policy to provide the right training to all key roles involved in information security and privacy. One key role in security policies is internal auditor, and we recommend the ISO 27001 lead auditor course for anyone involved in the internal audit programme. This is…
Floris van den Broek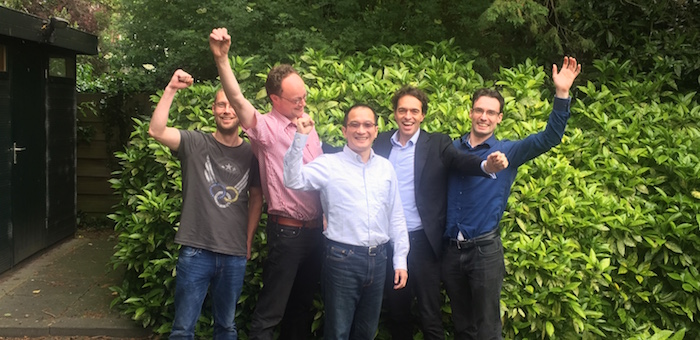
All candidates pass the ISO 27001 lead auditor exam
Congratulation to the candidates of our recent ISO 27001 lead auditor course. All candidates (Jan-Jasper, Joost, Floris, Sieuwert) that participate in this five day course have passed the exam. They can now call themselves IRCA certified information security auditors and are well equipped for key roles in information security teams.
Sieuwert van Otterloo