Blog Security
ISMS Auditor/Lead Auditor Training
ICT Institute organises the ISMS Auditor/Lead Auditor Training from 15-19 May in Amsterdam. This training is officially certified by CQI/IRCA (Chartered Quality Institute / International Register of Certified Auditors). CQI/IRCA is the world’s largest international certification body for auditors of management systems. Interested attendees may contact ICT Institute for details. Prior auditing experience and training is…
Floris van den Broek
A summary of ISO 27001 requirements for information security
ISO / IEC 27001 is an official standard for the information security of organisations. Regrettably the standard is not freely available, making it harder than necessary to look up what is actually required by ISO 27001. This has led to some misconceptions. While we still recommend you to read the full standard, we decided to create a good summary to…
Sieuwert van Otterloo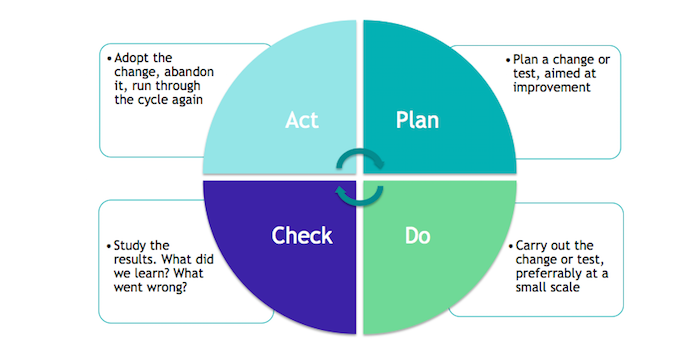
Information security and PDCA (Plan-Do-Check-Act)
Standards such as ISO 27001 require you to use a method for continuous improvement in your information security policy. PDCA or Plan-Do-Check-Act is the preferred method for most information security teams and we recommend you to use this method, described in this article.
Sieuwert van Otterloo
Information security – Cryptographic controls policy example
Using cryptographic controls such as encryption can help with information security, but only if it is applied correctly. To make sure it is used in the right way, it is recommended by standards such as ISO 27002 have a data encryption policy. In this article we share the ICT Institute data encryption policy, that is…
Sieuwert van Otterloo
Information security – asset inventory
One of the first steps in setting up an information security management system is to create an inventory of information assets. It is in important step to make sure the right measures will be taken: the assets are the basis for identifying risks, and thus for the measures that will be taken to mitigate risks.
Sieuwert van Otterloo