Blog
A basic risk management method for information security
One of the requirements for good information security is to have a method for risk identification and assessment. This article describes one simple and practical method that can be used by any organisation. This page is part of a series on ISO 27001 controls and our free ISO27001 and GDPR templates.
Sieuwert van Otterloo
ICT Institute is now a Vanta partner: what users told us
At ICT Institute, we support customers with all kind of tooling: classic self-contained templates, Google Workspace, Notion and now Vanta. For our clients that work towards ISO 27001, we can now combine our hands-on ISMS advice (scoping, risk workshops, internal audits) with a compliance platform that takes a lot of the manual effort of collecting…
Pavlo Burda
Implementing ISO 42001: example audit report
In our previous article on the AI Risk Management System, we explained how an AIMS can help organizations structure AI governance and support compliance efforts with the AI Act. Here we introduce our new template for auditing and structuring your AIMS and prepare for ISO 42001 certification. What is the AIMS? ISO 42001 requires organizations…
Pavlo Burda
The AI Act Risk Management System
In this article we explain what an AI Risk Management System (RMS) is, and why it is required by the AI Act for high-risk AI systems. We outline the components of the AI RMS and how you can potentially leverage, for example, your existing ISO 27001 work for ISO 42001 compliance. The AI Act:…
Pieter t Hoen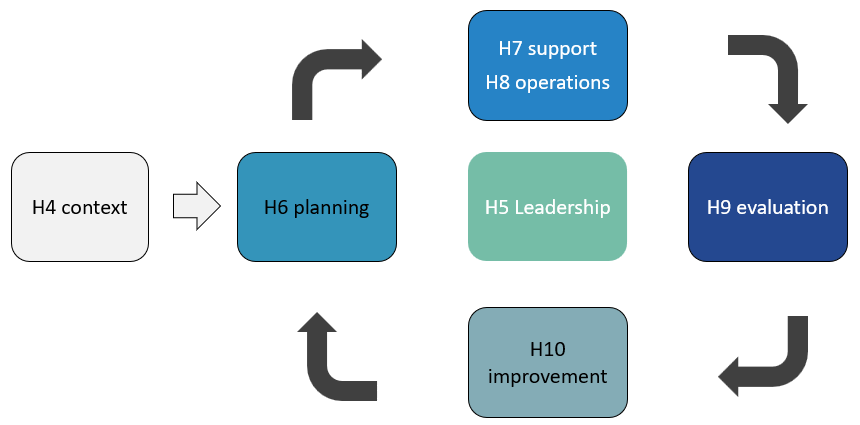
The ISO 27001 Harmonized Structure
In this article, we walk through the Harmonized Structure of the ISO 27001 (Chapters 4-10) and explain how to implement it using the Plan-Do-Check-Act (PDCA) cycle. This will be the basis for your Information Security Management System (ISMS) according to the standard. The “engine” of the ISMS: Chapters 4 to 10 ISO 27001 is structured…
Pavlo Burda